Why is the WAN source IP not showing on internal servers of a NAT rule?
Options

Zyxel_Emily
Posts: 1,499
 Zyxel Employee
in Networking
Question:
A customer using NAT rules observed that incoming traffic to their internal servers doesn't display the original WAN client source IPs. Instead, it shows the local interface private IPs.
Answer:
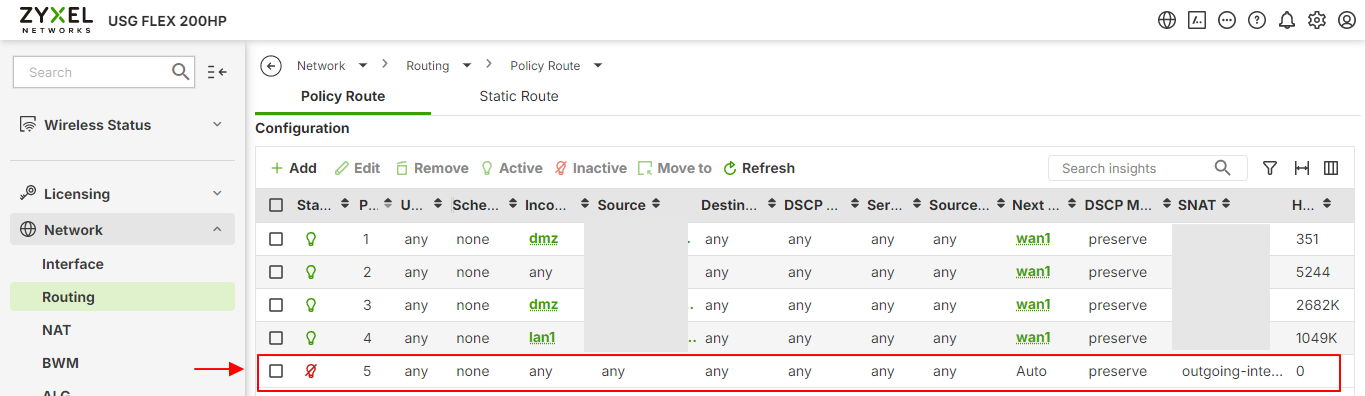
It may be affected by a policy route rule. This rule was set as 'incoming any, source any, destination any,' which led to the NAT traffic not functioning as expected. After disabling the problematic policy route rule, the correct external IPs appeared in the packet trace.
Tagged:
0
Categories
- All Categories
- 442 Beta Program
- 3.1K Nebula
- 242 Nebula Ideas
- 6.8K Security
- 764 USG FLEX H Series
- 385 Security Ideas
- 1.8K Switch
- 87 Switch Ideas
- 1.5K Wireless
- 58 Wireless Ideas
- 7.2K Consumer Product
- 323 Service & License
- 522 News and Release
- 100 Security Advisories
- 31 Education Center
- 10 [Campaign] Zyxel Network Detective
- 5.3K FAQ
- 34 Documents
- 91 About Community
- 121 Security Highlight